

atsec information security
Company
Our mission is to provide our customers with professional and independent advice on information security that empowers their business and operations.
Our Principles
Founded in January 2000, atsec has since grown into an international company with offices around the world, an experienced staff, and a service portfolio that encompasses almost every aspect of information security assessment, testing, and evaluation.
From our very first project to our current global business activities, we have always followed these principles:

We know the business
Privately owned and globally trusted, atsec accredited labs are global leaders in evaluating and testing complex software-based IT systems for vendors and for government agencies.


We stay focused
atsec colleagues are information security experts. As such, atsec focuses solely on security assessments, testing, and evaluations. We do not provide services in any other areas, and we do not sell hardware, software, or any other ware.

We are independent
We are not affiliated with any hardware or software vendor, and we never will be. Our customers rely on us to be objective, so our credibility as security experts hinges on that independence. We have no interest in selling anything other than our security assessment, testing, and evaluation expertise.
Our history
Exclusively specialized in information security, atsec has grown since it was founded in January 2000 into an international company with offices in the United States, Europe, and Asia.
Everybody shares the same vision, passion for IT security, and conviction that neutral and customer-oriented IT security services can only be provided by a company that is independent of products, vendors, outside capital, government agencies, and outside ownership.
atsec’s strength is its independence, and our history is built on that independence.
For the Community, With the Community
When atsec was founded, the cybersecurity field was much smaller, with fewer labs, less frequent international collaboration, and not as many products being made each year. The community was small, but tight-knit.
Fast forward to today, and most of that has changed. The community has grown, alongside the importance of cybersecurity, and atsec believes that keeping the community tight-knit as it continues to grow is important.
In 2013, we founded the International Cryptographic Module Conference as a way to strengthen those bonds, bringing together professionals and academics across all walks of the industry – it was described as a “win, win, win” for all parties involved. More recently, we realized we needed to expand that further to uplift newer generations of cryptographers and cybersecurity analysts, so we organized some accessible boot camps, wrote a book for practitioners of any experience level, and most recently helped found the Cypto-V Alliance.
We don’t know what the future will bring, but we do know the community will face it together. atsec will be there to do what we can every step of the way.
Our Contributions:
Past events atsec organized or contributed to:
FIPS ‘n’ Chips – A CVA Conference
Oct. 26-27, 2026, Austin, TX, US
Mar. 25th, 2025, Austin, TX, US
Feb. 27th, 2024, Austin, TX, US
Tasting Cryptography:
FIPS ‘n’ Chips
A practical guide to cryptographic standards, module validation, testing methodologies, implementation challenges, and industry best practices.
The Information Security Provider
Read Our Latest Blog Articles
Learn the latest and greatest about information security. You’ll find insights and analyses of recent developments in technology and policy on our blog.
-
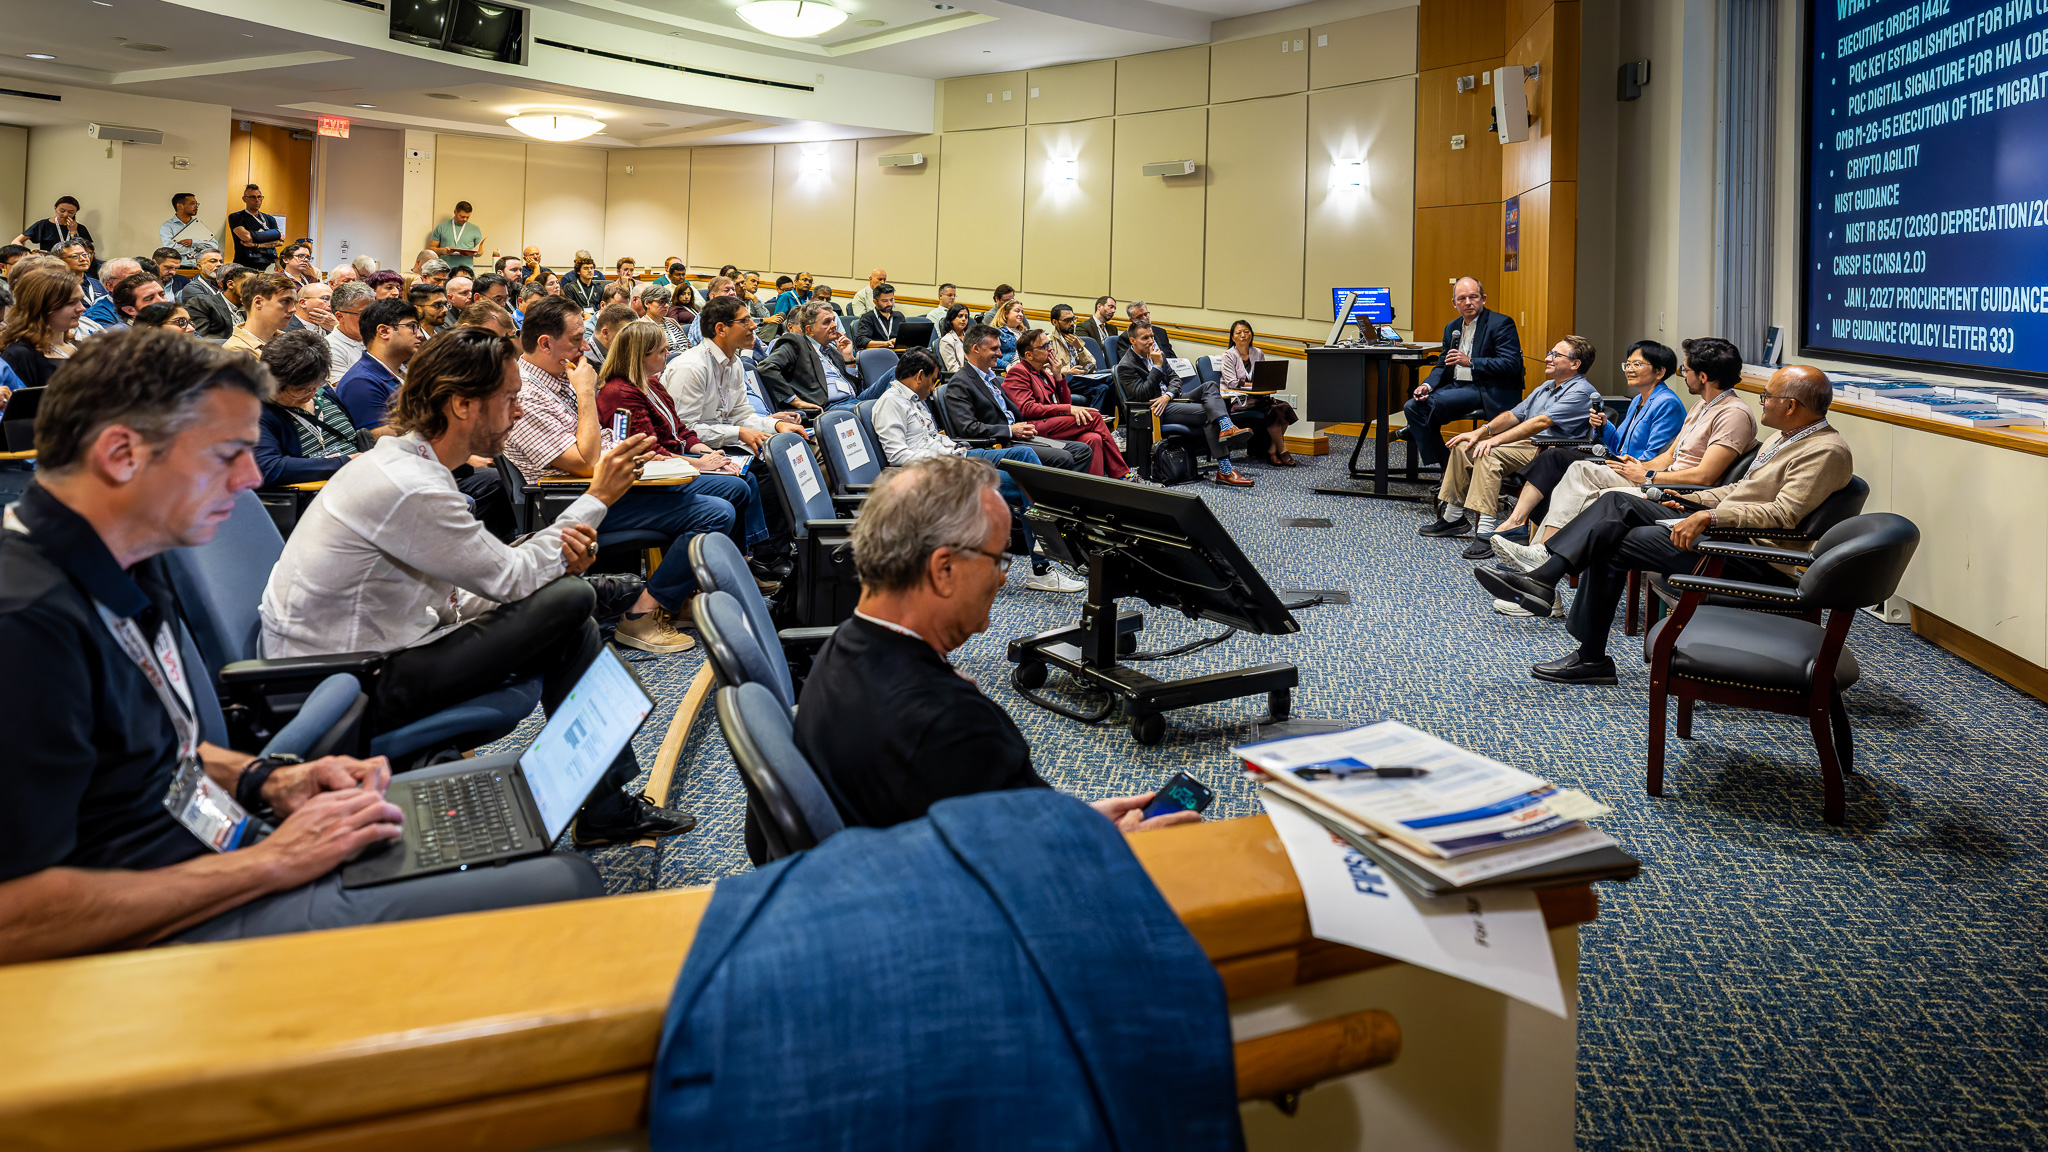
Making the Future Accessible at FIPS ‘n’ Chips 2026
FIPS ‘n’ Chips was a huge success, and part of its magic was its accessibility.
-
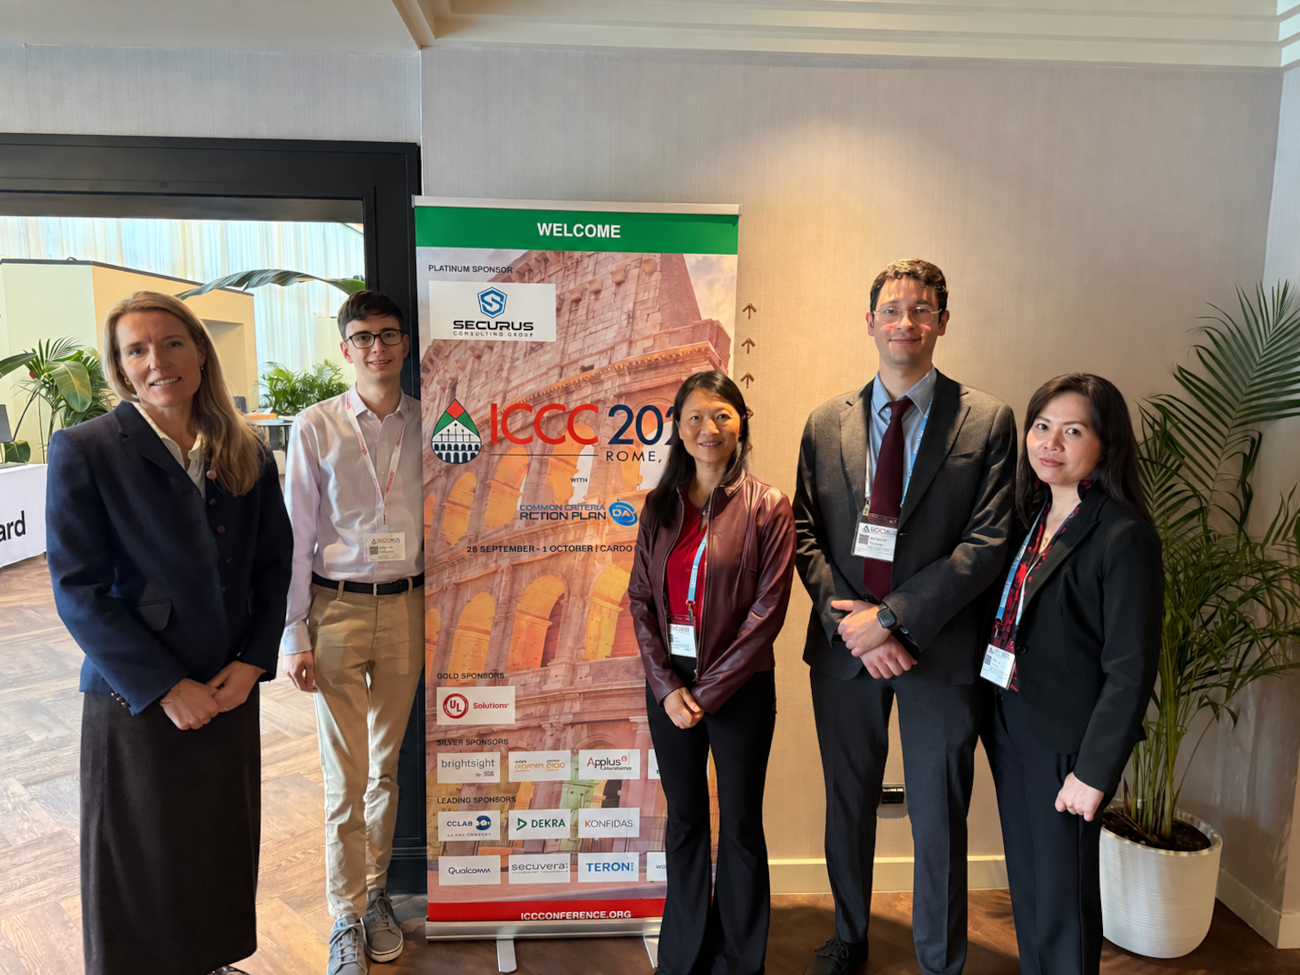
From the Forum to the Future: atsec Sponsors the 30th CCUF Workshop in Rome
On September 25, 2026, the Common Criteria community gathered in Rome for the second day of the 30th CCUF Workshop.

atsec information security
Join our team!
Seeking a new challenge? We are a dedicated team in a fast-growing market. Send us your application.